Archive for internet security

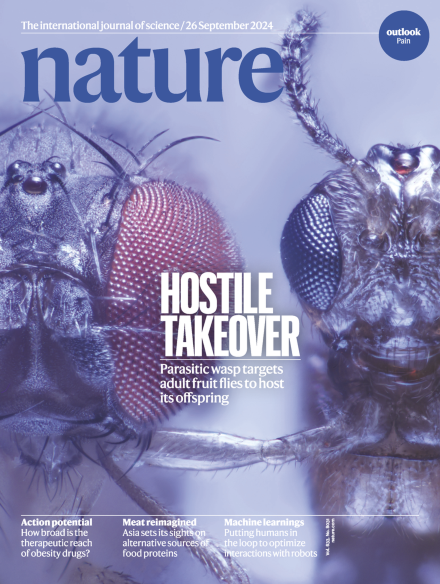
[not so] hostile takeover on my Nature issue

Posted in Books, pictures, Travel, University life with tags , , , , , , , , , , , , , , , , , , , , , , , , , , , , on November 29, 2024 by xi'an

When flying to Montréal last week, I took with me this 16 September issue of Nature but forgot it in the plane. But had time to read a tribune warning on the dangers of governments being involved in running the Internet. And thus disrupting its decentralised structure… And a short highlight on the (minimal) impact of atom-sized, asteroid-mass black holes crossing the Solar System, awakening me to the very existence of such stellar objects! And remained skeptical at the proposal to downsize pint glasses to lower beer consumption in the UK. (Although I now find myself unable to drink a whole pint of beer, outside eating a fiery curry! Or an alcohol free version.) And read how NobAIl Prize winning Alphafold2 unfolded a structure common to a family of flavivirus that make them relative with a common ancestor. And a book review pondering whether or not AI can feel distress, pondering at their sentience. (The book is freely available on OUP webpage.) Unlikely to be re-reviewed for CHANCE! And a fairly interesting long comment on how some Asian nations are massively investing into alternative approaches to meat production. (In particular since mentioning Singapore, where the company employing one of my nephews is soon to introduce in-vitro foie gras.) But missed the research paper on the origin and evolution of the bread wheat D genome, which I would have most certainly devoured, despite my favouring rye and buckwheat breads! (No bread was hurt in the study, since the 60 wheat landraces analysed therein came from the CIMMYT and ICARDA gene banks.) The origin is thus most likely on the “southern shores of the Caspian Sea 8,000–11,000 years ago”. Which sounds quite recent, all things considered!

corporate smokescreen

Posted in University life with tags , , , , , on January 8, 2021 by xi'an

Warwick U had all its staff going through an endless list of compulsory (under threat of being cut from the local system) “training” modules that droned through fairly elementary notions of computer safety and data protection for hours. With a compulsory quiz associated with each module that cannot be taken without “listening” to the entire thing. Given the absence of any real training provided by this enormous waste of staff time (since I presume the modules can be completed during working hours!), I wonder at the purpose of this corporate exercise, beside checking all the boxes to achieve legal protection in case of a data breach or another disaster… (For certain, nothing meaningful can be inferred from the policy pages attached to the exercise, as they are written in newspeak with enough acronyms to incapacitate a brand new typewriter!)